Regulatory Alignment: How NIS2, DORA, ISO 27001, and the EU AI Act Affect Vendor AI
Regulatory Alignment: How NIS2, DORA, ISO 27001, and the EU AI Act Affect Vendor AI explains where the rules overlap, differ, and shape smarter controls.
Introduction: Vendor AI Can Look Safe
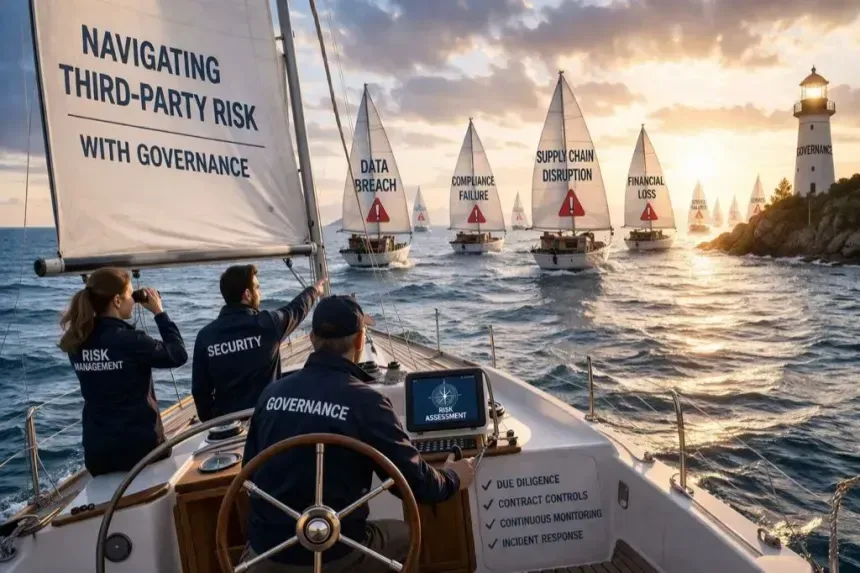
Vendor AI can pass procurement and still leave you exposed. The risk usually shows up later, when a model changes, a workflow breaks, or logging turns out to be too thin for audit use.
That is why Regulatory Alignment: How NIS2, DORA, ISO 27001, and the EU AI Act Affect Vendor AI matters for fintech and financial services teams. In this guide, you will see how the four regimes overlap, where they differ, and how to turn that into one vendor lifecycle control model.
The Real Regulatory Problem
Step 1. Define the vendor AI risk surface
Vendor AI risk lives in the stack, not just in the contract. It can enter through model outputs, training data, prompts, APIs, workflow automation, and the human review step that is supposed to catch bad calls.
Third-party AI is different from in-house automation because you do not control the full system. A vendor may change the model, add a sub-processor, or revise logging without making that visible in your business process.
That is where most failures happen. Weak oversight, thin audit logs, and fuzzy accountability make it hard to prove who approved what, when, and on what basis. For role definitions, the EU’s AI Act definitions and the AI Act Service Desk are good starting points.
Step 2. Why point-in-time reviews fail
A one-time vendor review is not enough. A vendor can pass a security check in one quarter and drift out of line the next after a model update, a data change, or a new sub-processor. That creates trouble for resilience and for evidence. If your records only show that you checked once, they will not show how you handled change over time.
This is where many teams get stuck. They treat approval as the finish line, then scramble when the vendor, the model, or the launch schedule moves.
Step 3. Reframe compliance as control design
The better question is not, “Which law applies?” The better question is, “What control do we need, who owns it, and how do we prove it works?” That shift matters because the goal is not to build four separate checklists. The goal is to turn legal duties into shared control families that work across procurement, legal, security, product, and compliance.
How The Four Frameworks Overlap
Step 1. Find the shared control themes
NIS2, DORA, ISO 27001, and the EU AI Act all point toward the same core ideas. They want governance, risk management, incident handling, documentation, and supplier oversight.
The wording differs, but the logic is similar. Each framework expects traceability and accountability. Each one asks you to show that your team knew the risk, made a decision, and kept evidence.
If you want the primary sources, start with the NIS2 Directive text, the DORA regulation, and ISO/IEC 27001. For AI screening, the Commission’s guidelines on prohibited AI practices help flag risky vendor features before onboarding.
Step 2. Separate the regulatory focus areas
NIS2 is centered on cyber risk and incident resilience. It is broad, but the message is clear: organizations need stronger security hygiene and supply-chain discipline.
DORA is more specific to financial services. It focuses on digital operational resilience and ICT third-party risk, which makes it especially important when vendors support live financial operations.
ISO 27001 gives you the control system for managing information security. The EU AI Act is different again. It focuses on AI-specific obligations like risk classification, transparency, and human oversight.
The DORA hub and ENISA’s NIS2 implementation guidance are useful if you need to turn legal text into operating controls.
Step 3. Spot where vendor AI creates tension
A vendor can be ISO 27001-aligned and still create AI Act exposure. That happens when the AI feature affects customer decisions or messages but lacks the right transparency or human review.
A vendor can also look resilient under DORA and still miss AI-specific needs like explainability or disclosure. That gap shows up fast when AI supports regulated decisions, customer interactions, or security workflows.
The AI Act Article 25 on value chain responsibilities matters here. So does the Commission’s guidance on transparency obligations. If you do not crosswalk these duties, you may approve a vendor for one reason and inherit risk for another.
Build A Vendor AI Governance Model
Step 1. Create one control taxonomy
The cleanest move is to group controls into five buckets: security, resilience, AI governance, documentation, and oversight.
That keeps legal, procurement, security, and compliance from building separate review tracks for the same vendor. It also makes it easier to compare vendors with one master control map instead of four scattered checklists.
A simple taxonomy looks like this:
- Security controls — access, encryption, logging, and vulnerability management.
- Resilience controls — failover, incident response, recovery timing, and continuity.
- AI governance controls — model change notice, human review, and transparency.
- Documentation controls — policies, test results, approvals, and audit trails.
- Oversight controls — monitoring, escalation, and periodic review.
For a U.S.-based reference, the AI Risk Management Framework gives teams a practical bridge between abstract duty and daily process.
Step 2. Assign owners and decision rights
Vendor AI issues get stuck when everyone is involved and no one is responsible.
Legal should own regulatory interpretation. Security should own technical validation. Product should own use-case scope. Compliance should own the control map and testing cadence. Engineering should own implementation details. Procurement should own contract mechanics.
That sounds basic. It is not. Most delays come from unclear handoffs, not from a lack of opinions. When your team needs speed, decision rights matter.
Step 3. Set review cadence and evidence standards
Annual renewal is too slow for vendor AI. Controls should be reviewed when the vendor changes materially, when your use case changes, or when you launch into a new market.
Evidence should include policies, logs, incident history, model change notices, control test results, and audit artifacts. If you cannot produce the proof fast, the control is weaker than it looks.
For oversight and evidence expectations, the DORA oversight guide is useful. The NIST AI Resource Center is also a good source when you need support materials for testing and implementation.
Due Diligence, Contracts, And Testing
Step 1. Tighten vendor due diligence
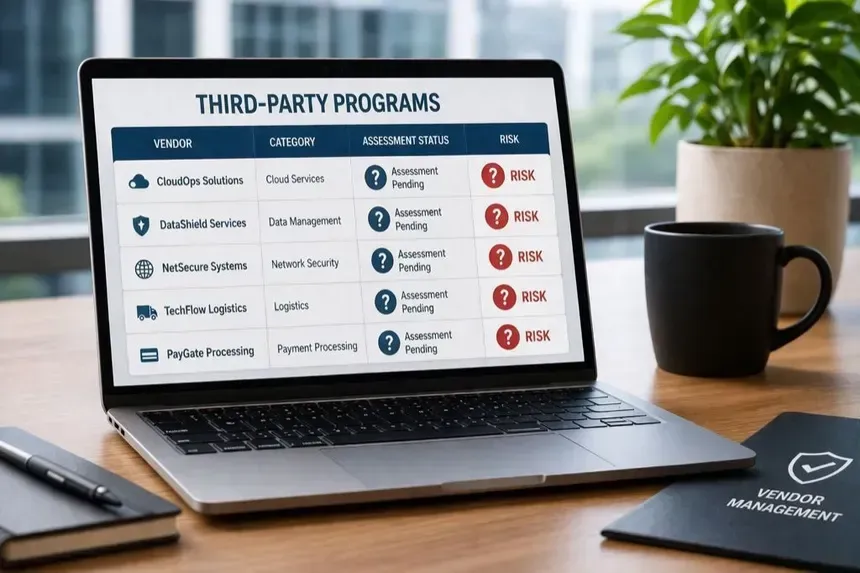
Before onboarding, verify the vendor’s AI use case, data handling, sub-processors, model governance, and incident response. Do not stop at the slide deck.
Ask whether the vendor is acting as a processor, service provider, or higher-risk AI supplier. That answer changes what you need in writing and what you need to monitor later.
A few good diligence questions are simple and direct:
- What model changes can happen without notice?
- What data is used for training, fine-tuning, or output improvement?
- Which human review steps are mandatory?
- What incidents trigger escalation?
- What logs can you provide on request?
Step 2. Put controls into contract terms
If a control matters, it should appear in the agreement. That means notice obligations, audit rights, logging requirements, security updates, and change management language. The contract should also cover model updates, data-use limits, and breach notification timing.
The point is not just to limit liability. The contract should support ongoing testing. If the agreement cannot support follow-up, it is too thin for regulated vendor AI.
Step 3. Test the vendor like regulators
Do not test only what the vendor says it does. Test what it actually does under pressure. Check change alerts, escalation paths, access controls, and output review procedures. Then confirm that the vendor can produce evidence quickly when your business needs it.
A simple test plan should answer three questions: Did the control run? Did it work? Can we prove it? If the answer to any of those is no, you have work to do before the next launch.
Conclusion
The main lesson is simple: do not manage NIS2, DORA, ISO 27001, and the EU AI Act in separate silos. Build one vendor AI governance system that covers shared controls, evidence, and review cadence.
That is the advantage of overlap. Once you standardize the process, you reduce rework and make launch decisions faster. The next move is practical: map one critical vendor, identify the gaps, and lock in the review process before the next release window opens.
FAQs
Q: What counts as vendor AI here?
A: It includes embedded models, AI-enabled workflows, and outsourced decision support. If the vendor influences a decision or output, it belongs in scope.
Q: Do all four frameworks apply at once?
A: Sometimes yes, sometimes no. The answer depends on the vendor, the use case, and the jurisdiction. In practice, the strongest obligation should set the baseline.
Q: Can ISO 27001 cover the AI Act?
A: No. ISO 27001 helps with security structure and documentation, but it does not replace AI-specific duties like transparency or human oversight.
Q: What is the fastest place to start?
A: Start with one vendor inventory, one master control map, and one evidence checklist. That gives you a working system without trying to solve everything at once.
Q: When should we bring in a specialist?
A: Bring in help when the use case is regulated, the launch crosses jurisdictions, vendor terms are still vague, or your audit evidence is thin. Those are the moments when general advice tends to stall.