AI as a New Source of Vendor Risk: Board Guide
AI as a New Source of Vendor Risk is a practical guide for boards and fintech leaders. Learn what to ask, how to monitor vendors, and how to govern AI wisely.
Introduction
AI vendor risk is board risk.
That is not a theoretical warning. It is what happens when a tool changes how decisions get made, how customer data moves, and how your team explains its actions to regulators.
In this guide, you will see where AI creates third-party exposure, what boards should ask, how to monitor vendors, and how to build governance that keeps launches moving without losing control.
Why AI Creates Vendor Risk
AI changes decision-making risk
Traditional SaaS usually creates software risk. If the tool goes down, slows down, or breaks a workflow, the fix is usually technical.
AI is different. It creates decision-making risk. A model can be “up” and still produce weak outputs, shaky explanations, or results that shift without warning.
That matters when the tool supports underwriting, fraud review, customer messaging, or compliance decisions. If the output is wrong, the business problem is not just a bug. It can turn into a customer issue, a legal issue, or a board-level issue.
NIST’s AI risk framework is useful here because it treats AI as a lifecycle issue, not a one-time purchase.
Hidden dependencies are easy to miss
AI vendors often sit on top of other vendors. They may rely on cloud services, model providers, sub-processors, APIs, and training data sources that your team never sees directly.
Those layers can change fast. A fintech might buy an AI fraud tool and assume the review logic is stable, only to learn the vendor changed a model, added a new data source, or routed data through a different sub-processor. That can change false positives, customer friction, and compliance risk in one move.
That is why AI security deserves board attention. NIST’s AI security and resilience work is a good public reference point when you need to think beyond the vendor demo.
Procurement does not catch it all
A standard vendor questionnaire can confirm insurance, uptime, and contract terms. It usually cannot tell you whether the model is explainable, whether the input data is biased, or whether the vendor can defend its outputs under pressure.
That is the trap. A clean file can create fake comfort.
Public resources help fill the gap. The FTC’s AI page, the CFPB’s black-box model guidance, and the NIST AI resource hub all point to the same idea: AI risk needs real oversight, not just a vendor file.
What Boards Need To Ask
Step 1. Map the use case clearly
Start with one simple question: what decision does this AI vendor support?
That answer changes everything. An internal drafting tool is not the same as a model that supports loan approvals, fraud screening, or customer disclosures.
If the tool touches customers, regulated decisions, or revenue, the oversight bar goes up fast. The board does not need to treat every AI tool like a top-tier risk. But it does need to know where the tool sits in the process and what happens if it gets things wrong.
The SEC’s AI governance discussion is a good reminder that use case context matters more than buzz.
Step 2. Test the data inputs
Next, ask what data the vendor uses, where it comes from, and how often it changes. This is where many AI issues start. If the model uses personal data, customer records, or a biased training set, the output can drift in ways that are hard to spot. That drift may not show up in a demo. It shows up later, when the numbers are off and nobody can explain why.
Ask whether the vendor limits data use, how it handles data changes, and whether the team can show input quality checks over time. The practical AI risk playbook can help teams turn those questions into a real review process instead of a one-time intake form.
Step 3. Demand an override path
Every AI vendor should answer one question plainly: who makes the final call when the output is wrong?
Boards should want to know whether humans can override the model, how exceptions are handled, and how the vendor documents escalations. If the vendor cannot explain that path, the board should slow down.
The Federal Reserve’s model validation and monitoring guidance is useful here because it makes one thing clear: models need limits, testing, and review. The CFPB has also stressed the need for specific AI decision explanations when consumer outcomes are involved.
Third-Party Due Diligence And Monitoring
Step 1. Expand vendor review standards
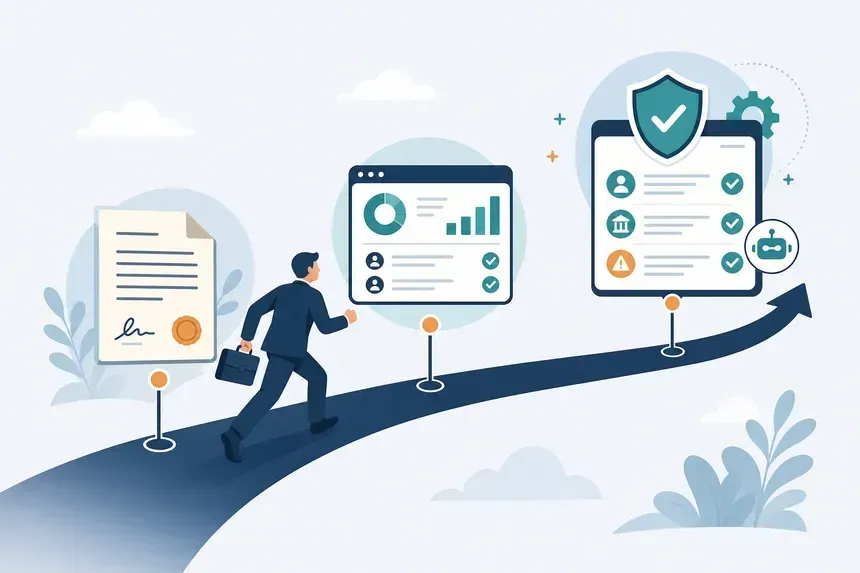
This is where AI vendor risk stops being a procurement issue and becomes a governance issue. The interagency third-party guidance and the Federal Reserve’s risk-based third-party oversight both support a lifecycle approach. That means review should cover onboarding, use, monitoring, and exit.
For AI vendors, add questions that go beyond standard due diligence:
- How transparent is the model?
- What testing has been done?
- What incidents have occurred?
- What security controls protect inputs and outputs?
- What changes require notice?
- What sub-processors or model providers sit behind the tool?
You should also compare vendor claims against public enforcement signals. SEC risk alerts are worth watching because they show where exam staff and enforcement teams are paying attention.
This is also the point where many teams realize they do not need more procurement checklists. They need someone who can define what “good” looks like for AI vendor review, monitoring, and escalation across the business.
Step 2. Set a real monitoring cadence
Boards should not review AI vendors on a one-size-fits-all schedule. Risk should drive the cadence.
A low-impact internal productivity tool may only need light monitoring. A model that affects customer approvals, fraud review, or compliance decisions needs a tighter review rhythm. Use triggers, not just dates.
Good triggers include:
- model updates
- new data sources
- complaint spikes
- incident reports
- new regulator guidance
- changes in output quality
Keep the artifacts simple. A dashboard, an issue log, and a quarterly board summary are usually enough to show what changed and what is being done about it.
Step 3. Build escalation rules
A good escalation path removes guesswork. Everyone should know when it goes to legal, compliance, risk, or the board.
If a vendor changes its model, misses a control, or cannot explain an output, that should trigger review right away. If the issue touches consumer harm, disclosures, or a regulated decision, escalation should move fast and be documented.
The point is not to create bureaucracy. The point is to stop teams from making up the response in the moment. That is when mistakes happen.
Governance That Actually Works
Step 1. Assign clear ownership
AI vendor governance falls apart when everyone thinks someone else owns it.
Procurement, legal, compliance, product, and risk all need a role. But no single team should carry the whole burden alone. A clean split helps:
- Procurement handles intake and commercial review.
- Legal reviews terms, liability, and disclosure risk.
- Compliance reviews regulatory fit and control design.
- Product owns use-case fit and user impact.
- Risk tracks ongoing exposure and escalation.
The CFPB’s AI governance structure is a good public example of how oversight can be organized across functions.
Step 2. Put controls in workflow
Governance should live inside the product lifecycle, not beside it.
If your team uses Jira, Notion, or Slack, build AI checks into intake, testing, launch, and post-launch review. That can mean a required approval before release, a testing checklist before a model update, and a post-launch review after complaints or exceptions.
That does not slow teams down. It cuts surprise issues later. And surprise issues are what kill release timing.
A little structure here goes a long way. If the process is buried in a policy nobody reads, it will not hold up when the team is under pressure. Put the control where the work happens.
Step 3. Use board reporting that matters
Keep board reporting short. Nobody needs a wall of text.
A useful report should show:
- risk level by vendor
- open issues
- remediation status
- upcoming model or data changes
- incidents, complaints, and exceptions
Keep the language plain. The board does not need jargon. It needs a clear view of what changed, what is stuck, and what needs attention next. If the report cannot answer those questions in a minute or two, it is too long.
Common Mistakes And Red Flags
Mistake 1. Treating AI like SaaS
This is the easiest mistake to make and the hardest one to unwind. A generic vendor checklist can miss model-specific risk, especially around explainability and customer impact. That is a problem when the tool influences decisions. The FDIC’s retired reminder that vendor models need model risk controls is on point here. If a vendor’s output affects a regulated decision, it belongs in a stronger review path.
Mistake 2. Ignoring change notices
An AI tool today is not guaranteed to behave the same way next quarter. Model updates, sub-processor changes, and new integrations can shift behavior quietly. If your team is not reading change notices closely, you may not notice the risk until a launch stalls or a regulator asks hard questions. That is a bad time to discover the tool changed.
Mistake 3. Skipping escalation rules
If no one knows when to escalate, issues get stuck. That creates delays, weak decisions, and messy regulator responses. It also makes the board look less informed than it should. Clear thresholds and named owners fix that. So does documenting what happens when a vendor cannot explain a result.
Conclusion
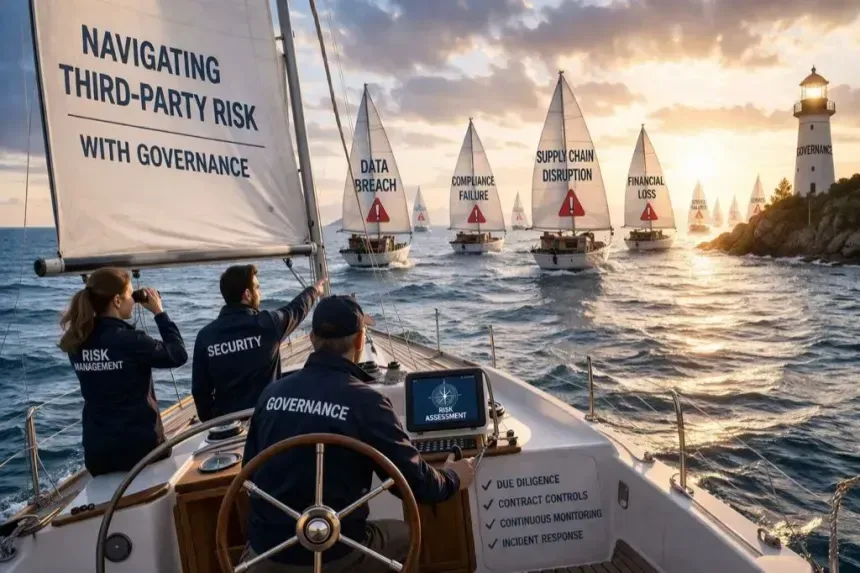
AI vendor risk is a governance problem, not just a procurement problem. Boards need repeatable review standards, a real monitoring cadence, and clear escalation paths if they want to keep launches moving without taking on hidden exposure.
Start with your highest-risk AI vendor. Close the biggest gaps. Then bring in senior compliance support if the team needs help setting the right standard before the next launch puts everyone under pressure.
FAQs
Q: Is AI vendor risk always a board issue?
A: No. Low-risk tools can stay with management. But if the AI tool affects customers, regulated decisions, or major operations, the board should have visibility. The higher the impact, the more senior the oversight should be.
Q: What should go in an AI vendor questionnaire?
A: Ask about data use, model updates, testing, incidents, human override rights, and change notices. Keep it tied to the actual use case. A fraud tool needs different questions than an internal writing assistant.
Q: How often should AI vendors be reviewed?
A: Use risk-based timing, not a flat calendar for every vendor. High-risk tools may need quarterly review or faster. Any model update, data change, or complaint spike should trigger an off-cycle check.
Q: What evidence should boards ask for?
A: Boards should ask for policies, test results, incident logs, monitoring reports, and change notices. Written evidence matters more than verbal reassurance because it shows how the vendor actually operates.
Q: When should escalation happen?
A: Escalate when a vendor changes a model, cannot explain an output, or misses a control. If the issue could affect consumers, disclosures, or a regulated decision, it should move quickly and be documented.
Q: Can a fractional CCO help with AI vendor risk?
A: Yes. A fractional CCO can help define review standards, set monitoring cadence, and create escalation rules without adding full-time headcount. That is often the fastest way to turn AI vendor risk into something the board can actually manage.