The End of Federal Disparate‑Impact Liability Under ECOA: What Lenders Must Change in 2026
This article breaks down underwriting, model governance, and monitoring fixes necessary under new ECOA guidance.
Introduction
The fair-lending playbook changed.
The end of federal disparate-impact liability under ECOA does not mean lenders can relax. Underwriting logic, model governance, pricing, servicing, and control gaps can still create enforcement risk, litigation risk, and board-level headaches. This guide breaks down what changed, what still matters, and what lenders should fix going forward.
What Changed Under ECOA
The CFPB’s 2026 Regulation B amendments removed the effects-test approach from the rule and stated that ECOA does not recognize disparate-impact liability the way many lenders had assumed for years. The rule text is on the CFPB’s 2026 Regulation B page, and the bureau’s broader ECOA resource hub is the cleanest place to track the agency’s current materials.
That is a real shift. But it is not a clean break from fair-lending risk.
The same data. The same policies. The same model outputs. They can still create problems if they show inconsistent treatment, weak documentation, or unexplained exceptions. If anything, the new rule puts more pressure on lenders to explain the why behind every decision.
The practical shift is simple: stop treating outcome alone as the whole story. Regulators, exam teams, plaintiffs’ counsel, and investors will still ask whether a policy is defensible, whether it is applied the same way every time, and whether the business can explain the reason for a denial, price difference, or override.
That is why the CFPB’s supervision manual and ECOA review procedures still matter. So do the OCC fair-lending handbook, the FDIC fair-lending manual, and the DOJ’s fair-lending resources.
Disparate Treatment Versus Outcome Claims
Disparate impact is about outcomes. It asks whether a neutral policy produces a harmful effect on a protected class, even without intent. Disparate treatment is about intent and treatment. It asks whether a lender treated people differently because of a prohibited basis.
That difference matters more now because lenders cannot point to a model result and call it done. A clean rationale, consistent exception handling, and a clear audit trail matter more than a polished policy deck. If the logic is messy, the defense will be messy too.
A neutral policy can still create real risk if it is poorly documented or applied inconsistently. For example, a cutoff that is used one way by operations and another way by underwriting will raise questions fast, even if the rule looks fine on paper.
What Still Creates Exposure
The loss of disparate-impact liability did not erase the rest of the fair-lending map. Unfair lending, redlining concerns, model bias, ECOA notice issues, and weak governance are still in play.
So are manual overrides, vendor decisioning, and post-booking servicing actions that are never reviewed with the same care as origination. A lender that says, “We dropped disparate impact, so we’re done,” is inviting trouble.
The Federal Reserve’s enforcement policy statement and the DOJ’s fair-lending enforcement page show that fair-lending scrutiny is still alive, just wearing a different hat.
Why 2026 Changes The Playbook
In 2026, teams need to rethink policy language, testing cadence, and escalation paths. The question is no longer just “Can this model survive legal review?” It is “Can this control survive launch pressure, audit review, and a board question on a bad day?”
That is a business issue, not just a compliance issue. If the answer is no, you get delayed launches, extra testing, and more firefighting than anyone wants.
What Lenders Must Change
Lenders should not just update the legal wording and move on. They need to redesign fair-lending controls around documented decisioning, explainability, and repeatable review.
Start with the policy stack. Fair-lending policies should reflect how decisions are actually made today. They should spell out who approves exceptions, what evidence is required for adverse decisions, and how escalations work when the answer is not obvious.
A policy that sounds good but leaves the workflow vague will not help much in an exam. Examiners and internal reviewers want to see what happens when the issue lands on someone’s desk at 4:45 p.m. on a Friday.
The operating model also needs a reset. Lending, legal, compliance, product, and data teams should share one definition of acceptable risk. If each group is using a different standard, the lender will end up with inconsistent thresholds and a lot of confusion about who owns the final call.
Here is a simple example. A fintech lender rolling out a new credit product may need to revisit income thresholds before launch. If those thresholds were inherited from an older product, they may no longer fit the current borrower mix, channel, or economics. That decision should be tested, documented, and signed off with a real business reason, not a shrug.
Rework Underwriting Controls
Underwriting controls should focus on cutoffs, overrides, and exception approvals. Review whether the same exception path is used the same way across teams, channels, and geographies.
Document the reason for each adverse decision. Keep the input data, the reason code, the override logic, and the approver in one place. That matters because a good-looking cutoff can still behave badly once it hits production.
This is also the place to test for proxy variables, drift, and unintended segmentation. If one channel starts approving far more exceptions than another, the issue may not be the policy. It may be the way the policy is being used.
Reset Model Governance
Inventory every model that affects credit decisions. That includes scorecards, ML tools, vendor models, pricing engines, and rules that act like models in practice. The Federal Reserve’s model risk management guidance is still the right anchor here.
Tighten approval, validation, and challenge steps before any material model change goes live. Keep independent review in the loop. Preserve the audit trail for every meaningful change.
If a vendor model is part of the stack, the lender still owns the risk. That is where a lot of teams get sloppy.
They buy a tool and assume the responsibility moves with it. It does not.
Update Fair-Lending Monitoring
Monitoring should stop feeling like a legal checkbox. It should act like a live control function with actual triggers and actual owners.
Set review points for denial rates, pricing differences, exception patterns, and model drift. If the product changes, the volume changes, or the borrower mix changes, the monitoring cadence should change too.
Use external benchmarks where they help. For mortgage portfolios, the CFPB’s HMDA data portal and the FFIEC’s HMDA data browser are useful for spotting patterns before examiners do.
How To Rebuild The Controls
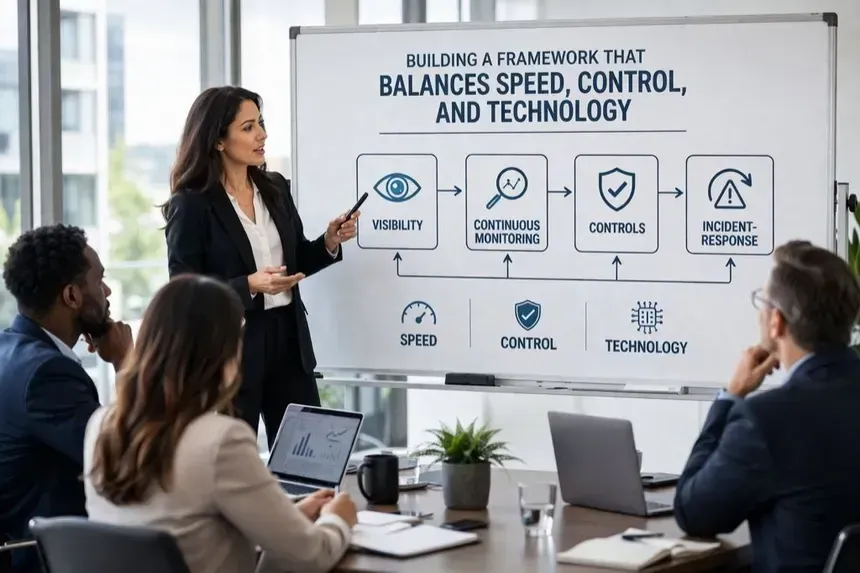
The fix is not a giant compliance binder. It is a control system that can move with the business and still hold up under review.
That means linking fair-lending monitoring to product design, underwriting QA, and issue management. If a new policy shifts denial rates or increases manual overrides, that signal should flow into the same tracker your ops and compliance teams already use.
Ownership matters too. Compliance should not carry everything on its back. Data science owns model logic. Operations owns execution. Risk owns escalation. Legal owns interpretation. Product owns release timing. If nobody can name the owner, the control is weak.
This is also where senior outside help can prevent expensive rework. A seasoned compliance lead can help turn scattered controls into something the team can actually run without turning every launch into a mini crisis.
Build A Clear Governance Stack
Assign clear accountability for policy, testing, remediation, and board reporting. A small lender does not need a room full of committees, but it does need names next to each control.
A practical setup might include a monthly working group for compliance, operations, and data, plus a quarterly review with legal and leadership. Keep it lean. Extra meetings do not equal better control.
Good governance is not more paperwork. It is clear ownership, clean evidence, and fast escalation when something looks off.
Strengthen Data And Testing
Review the datasets you use for completeness, integrity, and representativeness. If your data is missing channel, geography, or override fields, your testing will be weak before it starts.
Test outcomes across proxies, geography, product type, and channel.
If you operate in mortgage or home-equity, HMDA data is still the market standard for peer comparison. If you are in consumer lending, the same logic applies even if the dataset changes.
Plug The Monitoring Gaps
The biggest blind spots are usually manual overrides, vendor decisioning, and servicing actions after booking. Many lenders watch origination closely and then go quiet once the account is live.
That creates false comfort. A borrower can pass underwriting and still get uneven treatment later in pricing, line management, or collections. If your team wants help rebuilding testing protocols and control maps, Comply IQ can help lenders do that without hiring a full-time fair-lending lead.
90-Day Implementation Plan
You do not need a perfect program before you start. You need a defensible one that gets better on a clear schedule.
The trick is sequence. Legal, compliance, product, and data teams should move in parallel, not in a long chain of handoffs. The goal is not to freeze launches. The goal is to stop flying blind.
Think of a fintech lender that just launched a new credit product. The product is live, but exception rates are inconsistent across channels. A 90-day plan gives the team a way to find the issue, fix the riskiest gaps, and lock the process down before the next release.
Days 1–30: Diagnose The Exposure
Inventory every model, policy, and rule that affects credit decisions. Review exception logs, underwriting files, and monitoring reports for patterns that do not make sense.
Map the control owners. Flag undocumented approvals, unclear thresholds, and spots where the same rule appears to be applied three different ways. Use Jira, Notion, or even a shared tracker if that is what the team already lives in.
The point is visibility. If the issue is hidden in email threads, it will take longer to fix than it should.
Days 31–60: Fix The Highest Risks
Prioritize the controls most likely to cause findings or launch delays. That usually means policy language, threshold logic, override approval, and gaps in monitoring data.
Revise the weakest policies first. Calibrate thresholds. Fill the testing gaps. Then check the assumptions against current external material, such as the CFPB’s ECOA resources or the OCC fair-lending handbook.
A client alert from a law firm or a recent regulator bulletin can also help confirm whether your approach is still in range. The point is not to copy it blindly. It is to make sure your fix is grounded in current expectations.
Days 61–90: Lock In The Workflow
Formalize the ongoing reviews, reporting, and escalation paths. Train the people who actually touch the process so they know what changed and why it matters.
Document the evidence you will need for exams before you need it. That means the logic, the approvals, the testing output, and the remediation history. If you are still building the process by hand every month, the workflow is not done.
This is also the right moment to bring in a senior partner if the team needs help holding the line. Comply IQ’s fractional CCO support can stand up the workflow, guide the testing rhythm, and keep the process running as volume grows.
Conclusion
The end of disparate-impact liability under ECOA is not the end of fair-lending discipline.
Lenders still need tighter underwriting controls, stronger model governance, and monitoring that holds up when someone asks hard questions. The teams that win in 2026 will not be the ones with the prettiest policy deck. They will be the ones that can explain their decisions, show their evidence, and fix issues before they become exam findings.
If your current setup feels dated, this is the time to review it. If you need help rebuilding the framework faster,
Comply IQ can help you do it with senior compliance support on demand.
FAQs
Q: Does this mean fair-lending risk is gone?
A: No. The legal theory changed, but the operational risk did not. Lenders still need defensible policies, consistent decisioning, and reliable monitoring.
Q: What should model owners do first?
A: Start with a full inventory of decisioning models and rank them by borrower impact. Document inputs, validations, and override logic before you change thresholds or release settings.
Q: Do small lenders need the same controls?
A: They need the same control logic, but not the same scale. A smaller lender can run a leaner program if it is disciplined, documented, and applied the same way every time.
Q: How often should monitoring run now?
A: Most lenders should run reviews monthly or quarterly, depending on volume and product risk. Add ad hoc checks after launches, model changes, or unusual shifts in results.
Q: Where does outside expertise fit?
A: Bring in senior help when policy redesign, testing design, or regulator-facing issues go beyond the team’s depth. A fractional compliance lead can fill the gap without the cost of a full-time hire.