Third Party Contract Provisions for AI Vendors
Third Party Contract Provisions for AI vendors can make or break a fintech launch. Learn which clauses to review for data use, audit rights, and accountability.
Introduction
AI contracts fail quietly. A tool can look harmless in a demo and still create problems once it touches customer data, model outputs, or regulated workflows.
Generic vendor templates were not built for that. They miss the details that matter most when you are dealing with AI, regulators, and real operational risk.
This guide gives you a simple way to review AI contracts before a vendor reaches production. The goal is to avoid last-minute legal scrambles and keep launches moving.
Why AI Vendor Deals Work Differently
AI contracts are not just about software access. They also cover how data is used, how models behave, and who answers when the output causes trouble.
That is why fintech teams need to think about accountability even when the vendor owns the tool. Regulators usually look at the company using the system, not just the company that built it. The NIST AI Risk Management Framework is a useful place to start if you want to see that risk across the full lifecycle.
AI also brings issues that standard SaaS terms often miss. Bias, weak explainability, prompt retention, and hidden subprocessors can all show up in the fine print.
A chatbot is an easy example. It may sound like a simple support helper, but if it gives the wrong answer about fees or complaint rights, that can create consumer compliance exposure. The CFPB’s research on chatbots in consumer finance shows why this matters.
The FTC has also made clear that AI claims cannot outrun the product itself. Its AI hub and guidance to keep your AI claims in check are worth bookmarking.
Data and model risk shifts
AI vendors often touch several kinds of data at once. Customer data, prompt inputs, training data, logs, and output data can each carry separate contract risk.
That is why the agreement should spell out who can use the data, for what purpose, and for how long. It should also cover outputs and derived insights, not just raw inputs. A basic software clause is usually too thin for that job.
Regulatory accountability stays with you
Outsourcing AI does not outsource legal responsibility. If the tool creates a misleading disclosure, a bad recommendation, or a confusing customer message, your fintech is still the one that may have to explain it.
That applies across banking, payments, lending, and marketing. The CFPB’s AI hub is especially relevant if the tool touches consumer finance, and the CFPB’s adverse action guidance is a useful reminder that complex systems still need clear reasons.
A Simple Review Framework
The fastest way to review AI contracts is to stop treating them like generic vendor paper. A better approach is to use a short review sequence for Third Party Contract Provisions that ties the contract to the actual use case.
This keeps founders, COOs, and general counsel on the same page. It also helps you avoid endless redlines that slow down procurement without improving the deal.
Use the same sequence before redlining, during vendor selection, and again at renewal. That way, the review supports launch speed instead of fighting it. For more practical guidance, the NIST AI RMF Playbook is a good companion.
Step 1. Map the use case
Start with the business purpose in plain English. Is the tool writing internal notes, supporting customer service, or influencing a decision that affects a consumer?
That answer changes the level of diligence. A low-risk writing aid is not the same as a model that touches onboarding, underwriting, or customer complaints.
Step 2. Classify the data
Next, sort the data into public, internal, confidential, and regulated buckets. PII, NPI, payment data, and complaint data should always get stricter treatment.
Use your internal policy or a simple data inventory to drive the review. If the data is sensitive, the contract should be strict on storage, access, and retention. The NIST Privacy Framework is a solid reference here.
Step 3. Match the controls
Once the use case and data are clear, make the contract match the risk. Higher-risk use cases should bring tighter training limits, faster incident notice, and stronger audit rights.
This is where compliance, product, security, and engineering all need a say. If the contract does not match your vendor risk program, it will not hold up well under pressure.
Clauses That Deserve Focus
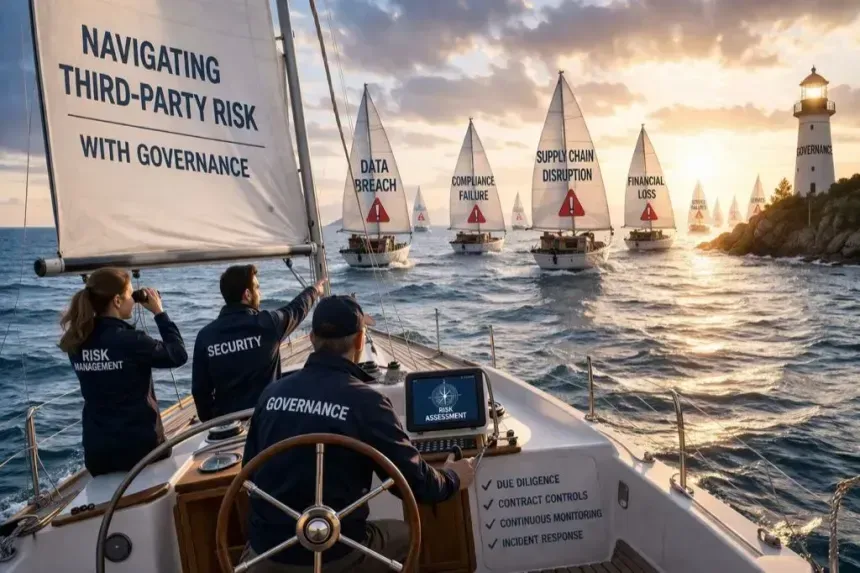
You do not need to spend weeks on every line. But Third Party Contract Provisions tied to data, oversight, and incident response deserve real attention. These terms shape how the vendor can use the tool, how you monitor it, and how you defend it if a regulator asks questions.
Data use and retention
The contract should clearly limit how the vendor can use your data. If you do not want customer data used for training, say that directly. Also define retention periods, deletion duties, backup exceptions, and where the data can be stored. If the vendor cannot explain those points clearly, that is a warning sign.
Audit rights and testing
Do not settle for vague assurances. You need enough visibility to show that the vendor’s controls actually exist. Ask for audit rights, SOC reports, and testing evidence where they make sense. If the tool affects a regulated workflow, it may also be worth asking for logs, model change history, and incident evidence. The FDIC third-party risk guidance is helpful here.
Subprocessors and third parties
AI vendors often rely on cloud hosts, model providers, and data processors. That chain can be longer than it looks on the sales call. Your contract should require notice of material subprocessors, flow-down obligations, and liability alignment. The Interagency Guidance on Third-Party Relationships and the OCC’s third-party bulletin both support that approach.
Output responsibility and disclaimers
Be careful with “for informational purposes only” language. That may be fine in some deals, but it can also weaken the vendor’s accountability when the output is part of the business process. If the tool supports regulated work, the vendor should stand behind reasonable accuracy, moderation behavior, or change logs where relevant. The FTC’s warning on AI claims is a good reminder not to let marketing language outrun reality.
Incident notice and remediation
The contract should say how fast the vendor must notify you about a breach, misuse event, or harmful model behavior. Slow notice can wreck a launch and leave your team guessing. You also want cooperation on investigations, consumer impact analysis, and regulator questions. When a problem hits, a clean escalation path is better than a long email thread.
A Fast Review Process
A good process keeps the deal moving and cuts down on rework. It also keeps legal from becoming the place where every issue lands at the last minute.
Step 1. Screen the vendor
Do a quick first-pass risk screen before full diligence. Ask what model is being used, what data it touches, and whether the use case affects consumers or regulated workflows. Also check basic security, privacy, and business continuity signals. If the vendor cannot answer simple questions clearly, escalate it.
Step 2. Redline the key terms
Focus redlines on the clauses with the biggest regulatory impact. That usually means data restrictions, audit rights, indemnity, and incident notice. Do not waste time rewriting low-value language that does not change the risk. A simple clause tracker can keep legal, compliance, product, and engineering aligned.
Step 3. Document the decision
Keep a record of the risk assessment, business rationale, and required controls. That matters later if an auditor, customer, or regulator asks why the vendor was approved. Link the contract review to onboarding and monitoring. Store the final position in a shared compliance repository so the next renewal starts with context, not guesswork. The NIST AI Resource Center is useful if your team wants more operating material.
Step 4. Monitor after signing
Contract review does not stop at signature. Set renewal checkpoints, issue logs, and periodic control testing. Revisit the agreement when the use case changes or the model is updated. That keeps the vendor aligned with your current risk posture.
Mistakes That Cause Trouble
The worst AI contract mistakes usually look small at the start. Then they show up later, after a complaint, a regulator question, or a product delay.
Relying on generic templates
A standard MSA does not cover model drift, retraining, or output errors very well. If you use boilerplate, update it with AI-specific terms instead of assuming the old language will stretch far enough.
Ignoring downstream accountability
“The vendor said it was compliant” is not a defense. You still need oversight, evidence, and one clear executive owner for the decision.
Skipping ongoing review
AI vendors change models, subprocessors, and terms over time. A one-time review is not enough, especially when the tool sits inside a consumer-facing or regulated process.
Conclusion
Strong Third Party Contract Provisions help fintech teams use AI without creating avoidable compliance headaches. The key is simple: tie the contract to the use case, the data, the clause review, and the monitoring plan.
If an AI vendor touches sensitive data or a launch-critical workflow, bring senior compliance help in early. That is often the difference between a clean launch and a mess you have to fix later.
FAQs
Q: What are third party contract provisions?
A: They are the contract terms that define risk, responsibility, and oversight between your company and a vendor. In AI deals, they matter more because data use, outputs, and model behavior can create compliance risk.
Q: What should be in an AI vendor contract?
A: Focus on data restrictions, audit rights, subprocessor notice, incident reporting, and output limits. The contract should also fit the specific business use case.
Q: Do I need special AI language in every vendor deal?
A: Not always. Lower-risk internal tools may need lighter drafting, but anything consumer-facing or regulated should get stronger AI-specific terms.
Q: Who should review AI vendor contracts?
A: Legal, compliance, security, product, and engineering should all weigh in. That cross-functional review helps catch blind spots before the contract is signed.
Q: How do I handle vendor pushback?
A: Lead with the highest-risk terms first and explain the business reason behind each ask. Some points are negotiable, but accountability, data controls, and incident response should not be.
Q: When should we revisit the contract?
A: Revisit it at renewal, after model updates, after use case changes, and after incidents or regulator inquiries. AI contracts need change checks, not just one-time approval.